The idea
NexaRad is a research foundation for radiology workflow software: backend-owned auth, tenant isolation, local DICOM services, object storage, structured findings, verifier-gated reports, and AWS-first infrastructure boundaries.
The problem
Medical imaging demos often skip the hard parts: PHI boundaries, DICOM plumbing, tenant isolation, object storage, report provenance, and clear labeling when something is research-only rather than clinical software.
How it works
I built a local stack with web, API, OHIF, Orthanc, MinIO, Alembic migrations, seeded non-PHI studies, synthetic upload smoke tests, demo/research safety defaults, and a rule that browser clients only call the NexaRad API.
System
Non-clinical imaging stack
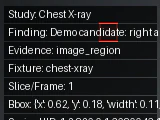
Browser clients call only the NexaRad API. PHI stays off; Orthanc and MinIO hold synthetic evidence.
OHIF/product frame with synthetic DICOM evidence and report provenance across Orthanc and MinIO.
The work
Demo / Research / Not for Clinical Use labels stay visible near every relevant claim. Idempotent `make seed` path and synthetic CXR fixtures.
Synthetic DICOM demo · PHI disabled · external AI off by default
Where it stands
The local walkthrough uses synthetic studies and draft reports to exercise the workflow. Patient data and external AI providers are disabled by default.
Demo / Research / Not for Clinical Use
Not for clinical use. Synthetic evidence only; no diagnostic claims.